Latest DevOps & Cloud News – 08 October 2026
📰 Top DevOps & Cloud Articles
OpenSSH 10.6 deliberately breaks two features in the name of security
Source : The New Stack
OpenSSH 10.6, released Tuesday, makes compression less effective and rejects some usernames that previously worked, and the maintainers knew both
The post OpenSSH 10.6 deliberately breaks two features in the name of security appeared first on The New Stack.
Claude’s cyber safeguards are getting more flexible — but not for everyone.
Source : The New Stack
This week, Anthropic announced an expansion of its Cyber Verification Program (CVP), breaking access into three use case–based tiers and
The post Claude’s cyber safeguards are getting more flexible — but not for everyone. appeared first on The New Stack.
Decision models are suddenly everywhere. OpenAI’s is now public.
Source : The New Stack
This week, OpenAI opened its Decisions API to public beta and added image inputs to make fast decisions from visual
The post Decision models are suddenly everywhere. OpenAI’s is now public. appeared first on The New Stack.
AI Is Taking on Entry-Level Engineering Work. Who Trains the Young Engineers?
Source : DevOps.com
 When I started my career on a support desk, I dealt with failed logins, missing permissions and recurring system errors every day. The work was repetitive, but repetition taught me to spot patterns, test assumptions and look beyond the symptom a user reported. Over time, I was resolving around 90% of incidents at first contact. […]
Three Truths About AI SRE
Source : DevOps.com
 The current enthusiasm for AI in Site Reliability Engineering (AI SRE) is well-founded. We are seeing incredible advancements in agents that can ingest alerts, parse logs, and propose rapid solutions to outages. They are becoming increasingly confident when it comes to suggesting bug fixes, patching vulnerabilities, and helping coordinate around
HackerOne Report Surfaces Massive Increase in Vulnerability Backlogs
Source : DevOps.com
 HackerOne research shows vulnerability remediation is getting faster, but AI-driven discovery is expanding exposure debt even more quickly, putting DevSecOps teams under growing pressure.
When the Scheduler is Full but the Autoscaler Is Not
Source : Container Journal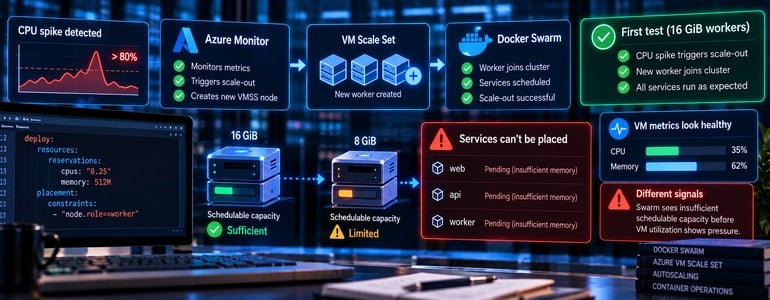
Docker Swarm autoscaling can look healthy at the VM layer while services remain unschedulable. Effective scaling needs scheduler capacity signals as well as host utilization.
The post When the Scheduler is Full but the Autoscaler Is Not appeared first on Cloud Native Now.
AKS Is Growing – Along With Its Kubernetes Utilization Problem
Source : Container Journal
AKS has become a major platform for enterprise Kubernetes workloads, and those workloads are getting more expensive. Organizations are running more compute, adding GPU infrastructure for AI, and expanding Kubernetes into more parts of their production environments. The problem is that the infrastructure underneath all of this is being used
The post AKS Is Growing – Along With Its Kubernetes Utilization Problem appeared fir
RapidFort Creates Multiple Alliances to Better Secure Cloud-Native Applications
Source : Container Journal
RapidFort, a provider of curated open source container images, has allied with both Wiz and Aqua Security to streamline DevSecOps workflows for organizations building and deploying cloud-native applications. Additionally, RapidFort has inked a cooperative research and development agreement with SpaceWERX, an arm of the United States Space Force (USSF) and
The post RapidFort Creates Multiple Alliances to Better Secure Cloud-Native Applications appeared first on
Attackers Hijack .gh, .sl, and .as Registries to Obtain Certificates for Google Domains
Source : The Hacker NewsAttackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6. Google's own systems were not breached, but any domain ending in .gh (Ghana), .sl (Sierra Leone) or .as (American Samoa) was put at risk. With such a certificate, an attacker could pose as the real site over an encrypted
Eight Malicious npm Packages Downloaded 40,767 Times Deliver Overlord RAT and Stealer
Source : The Hacker NewsCybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans (RAT) to compromised hosts. The campaign has been codenamed MALFEX by CloudSEK and Checkmarx. The activity is assessed to be the work of a lone threat actor who appears to have published 12 packages since August 2023, eight of which have
SonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Appliances
Source : The Hacker NewsSonicWall has released hotfixes for four flaws in its SMA1000 appliances, the gateways that give remote workers access to a company's network and applications. The most serious could allow an attacker without a login to send requests through the appliance and reach internal functions. SonicWall rates it 10.0 on the CVSS scale and says it has no evidence that any of the four flaws is being


